Single Sign-On (SSO)
Purpose
This document explains how to connect Azure Active Directory SSO to Xecta product platform(s) using SAML2.0.
Need help? Contact Support
Other Readings: Azure Enterprise Applications, About AWS Cognito, Azure AD integration with AWS Cognito
Overview
The Xecta product platform uses AWS Cognito to manage customer identity and access management (CIAM). To enable customer initiated SSO via Azure AD the customer must create and configure an Azure Enterprise Application. The tutorial below explains each step to create and configure the Enterprise Application. To complete this tutorial the person must have Azure privileges to administer Enterprise Applications
Tutorial
1: Register Xecta as an Azure Enterprise Application
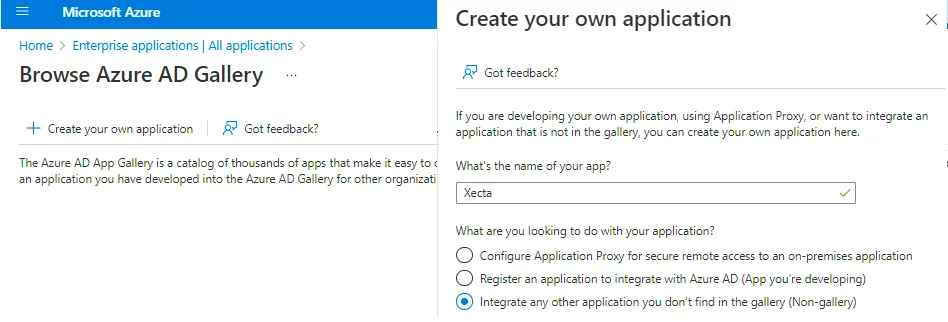
As an Azure Administrator open the portal.azure.com and navigate to Enterprise Applications. Select Create new application. Select "Integrate any other application (non-gallery)" Use "Xecta" as the application name.
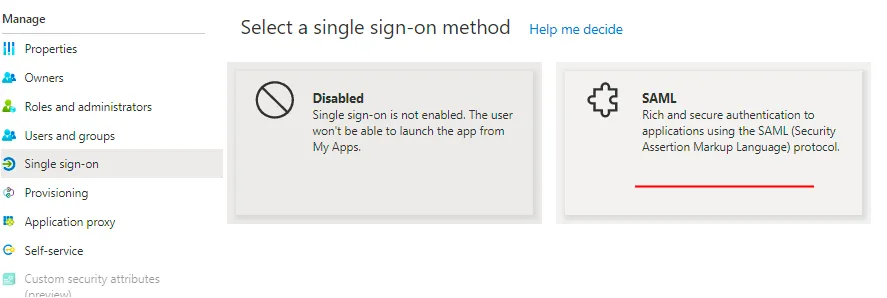
2: Setup SAML Integration
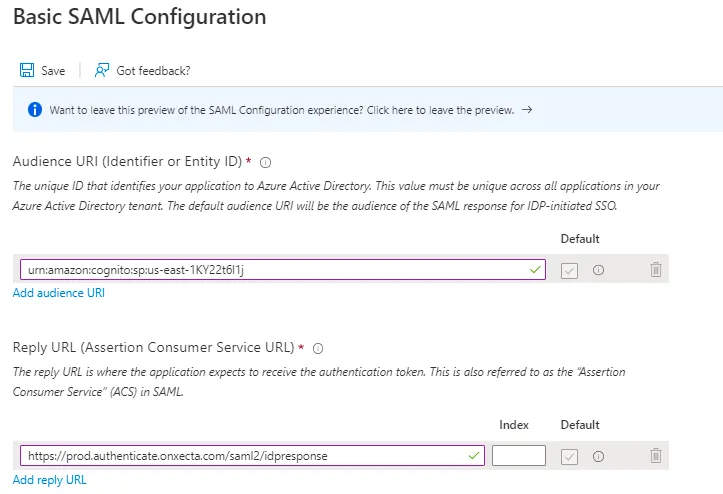
SAML Configuration Values
Reply URL: https://prod.authenticate.onxecta.com/saml2/idpresponse
Identifier: urn:amazon:cognito:sp:us-east-1_KY22t6l1j
3: Generate Federation Metadata XML file
Download the Federation Data XML file
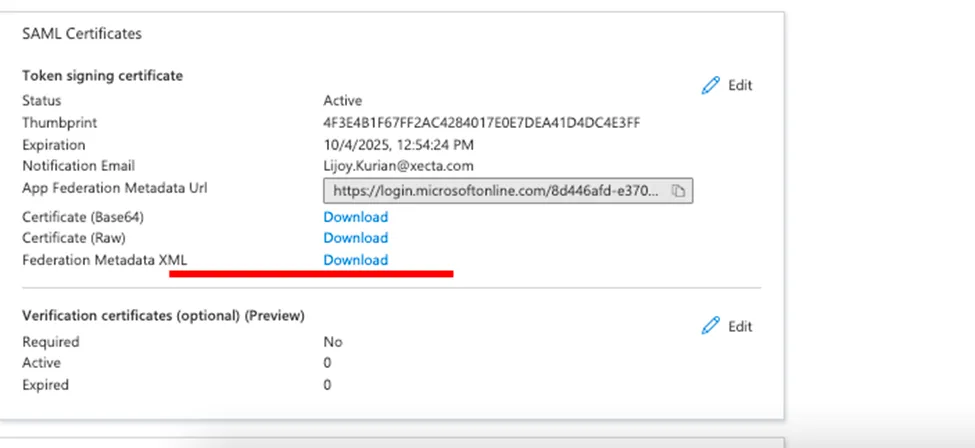
4: Secure Upload of Federation Metadata XML file
Upload the file to the Xecta Secure File Transfer system. Contact or your customer account representative to gain access to the Secure File Transfer System. Once you have access drop the XML file into the drop zone and submit the file. Secure file transfer is provided by SendSafely. Support will provide you with a dropzone URL similar to https://xecta.sendsafely.com/dropzone/aaa.bbb.ccc
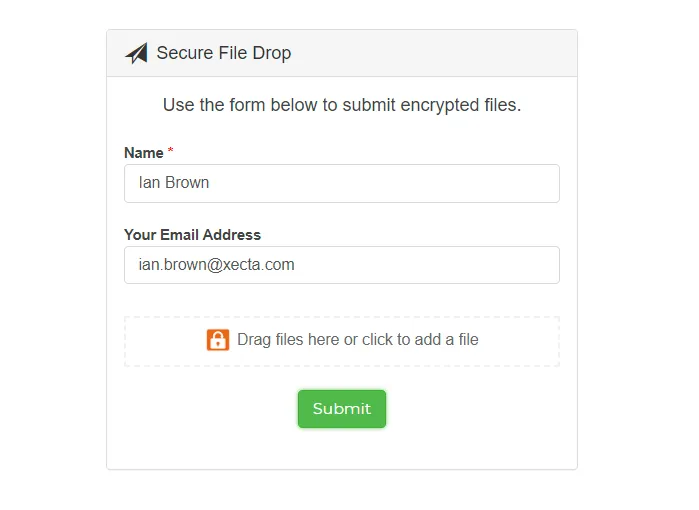
You will get notified by email once SSO has been setup on your account.
5: Test SSO Integration
Once SSO integration is complete test the Federation setup using the "Test" at the bottom of the Azure SAML configuration screen
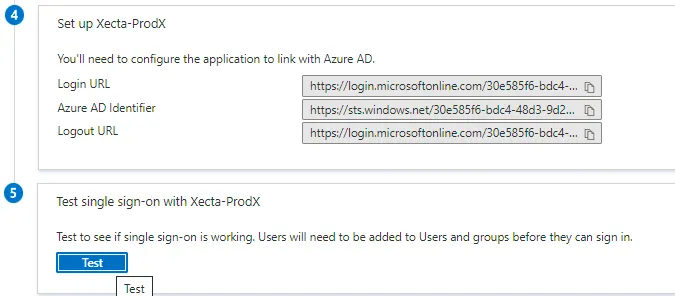
6: Authorize Azure AD Users or Groups to access the Xecta Enterprise Application
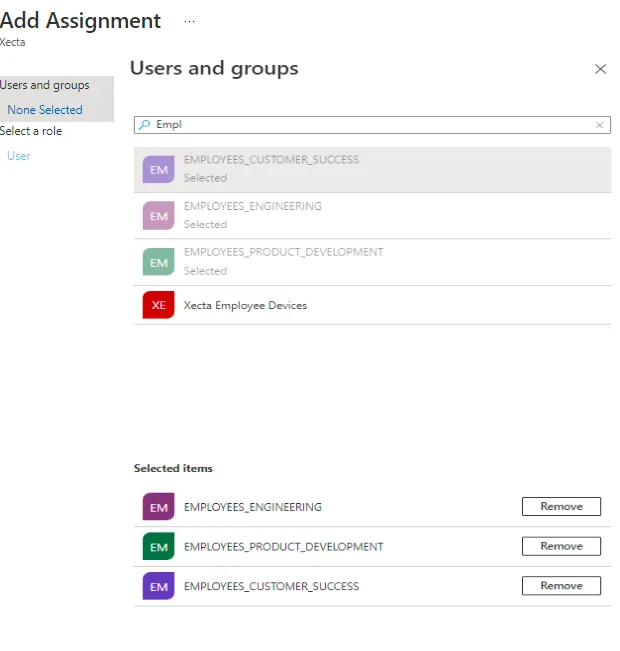
Select "Users and Groups" from the left hand menu
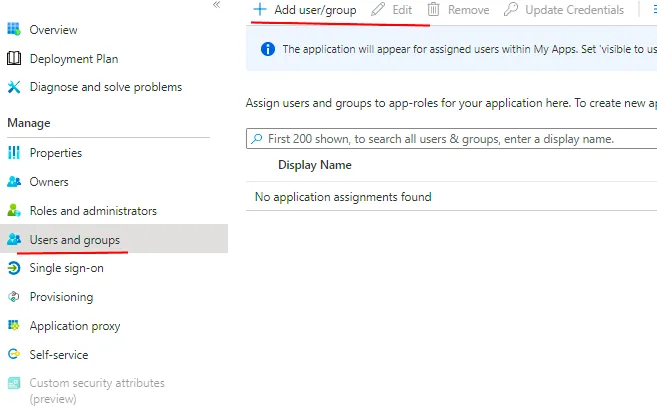
Add a user and or groups using the Azure AD user/group search box provided. Save when complete. These users or groups will be permitted to access the Xecta Product Platform via SSO